No items found.
No items found.

Our mission is to make every company harder to hack

Our Story

Rogier Fischer and Olivier Beg met on an online forum in 2009. They were 13. Within a few years they were working as white-hat hackers for Dutch banks and global tech companies, and they watched attackers start using automation and AI while red teams still worked by hand.

‍

In 2021, they founded Hadrian in Amsterdam with Maurice Clin to put that technology on the defenders' side.
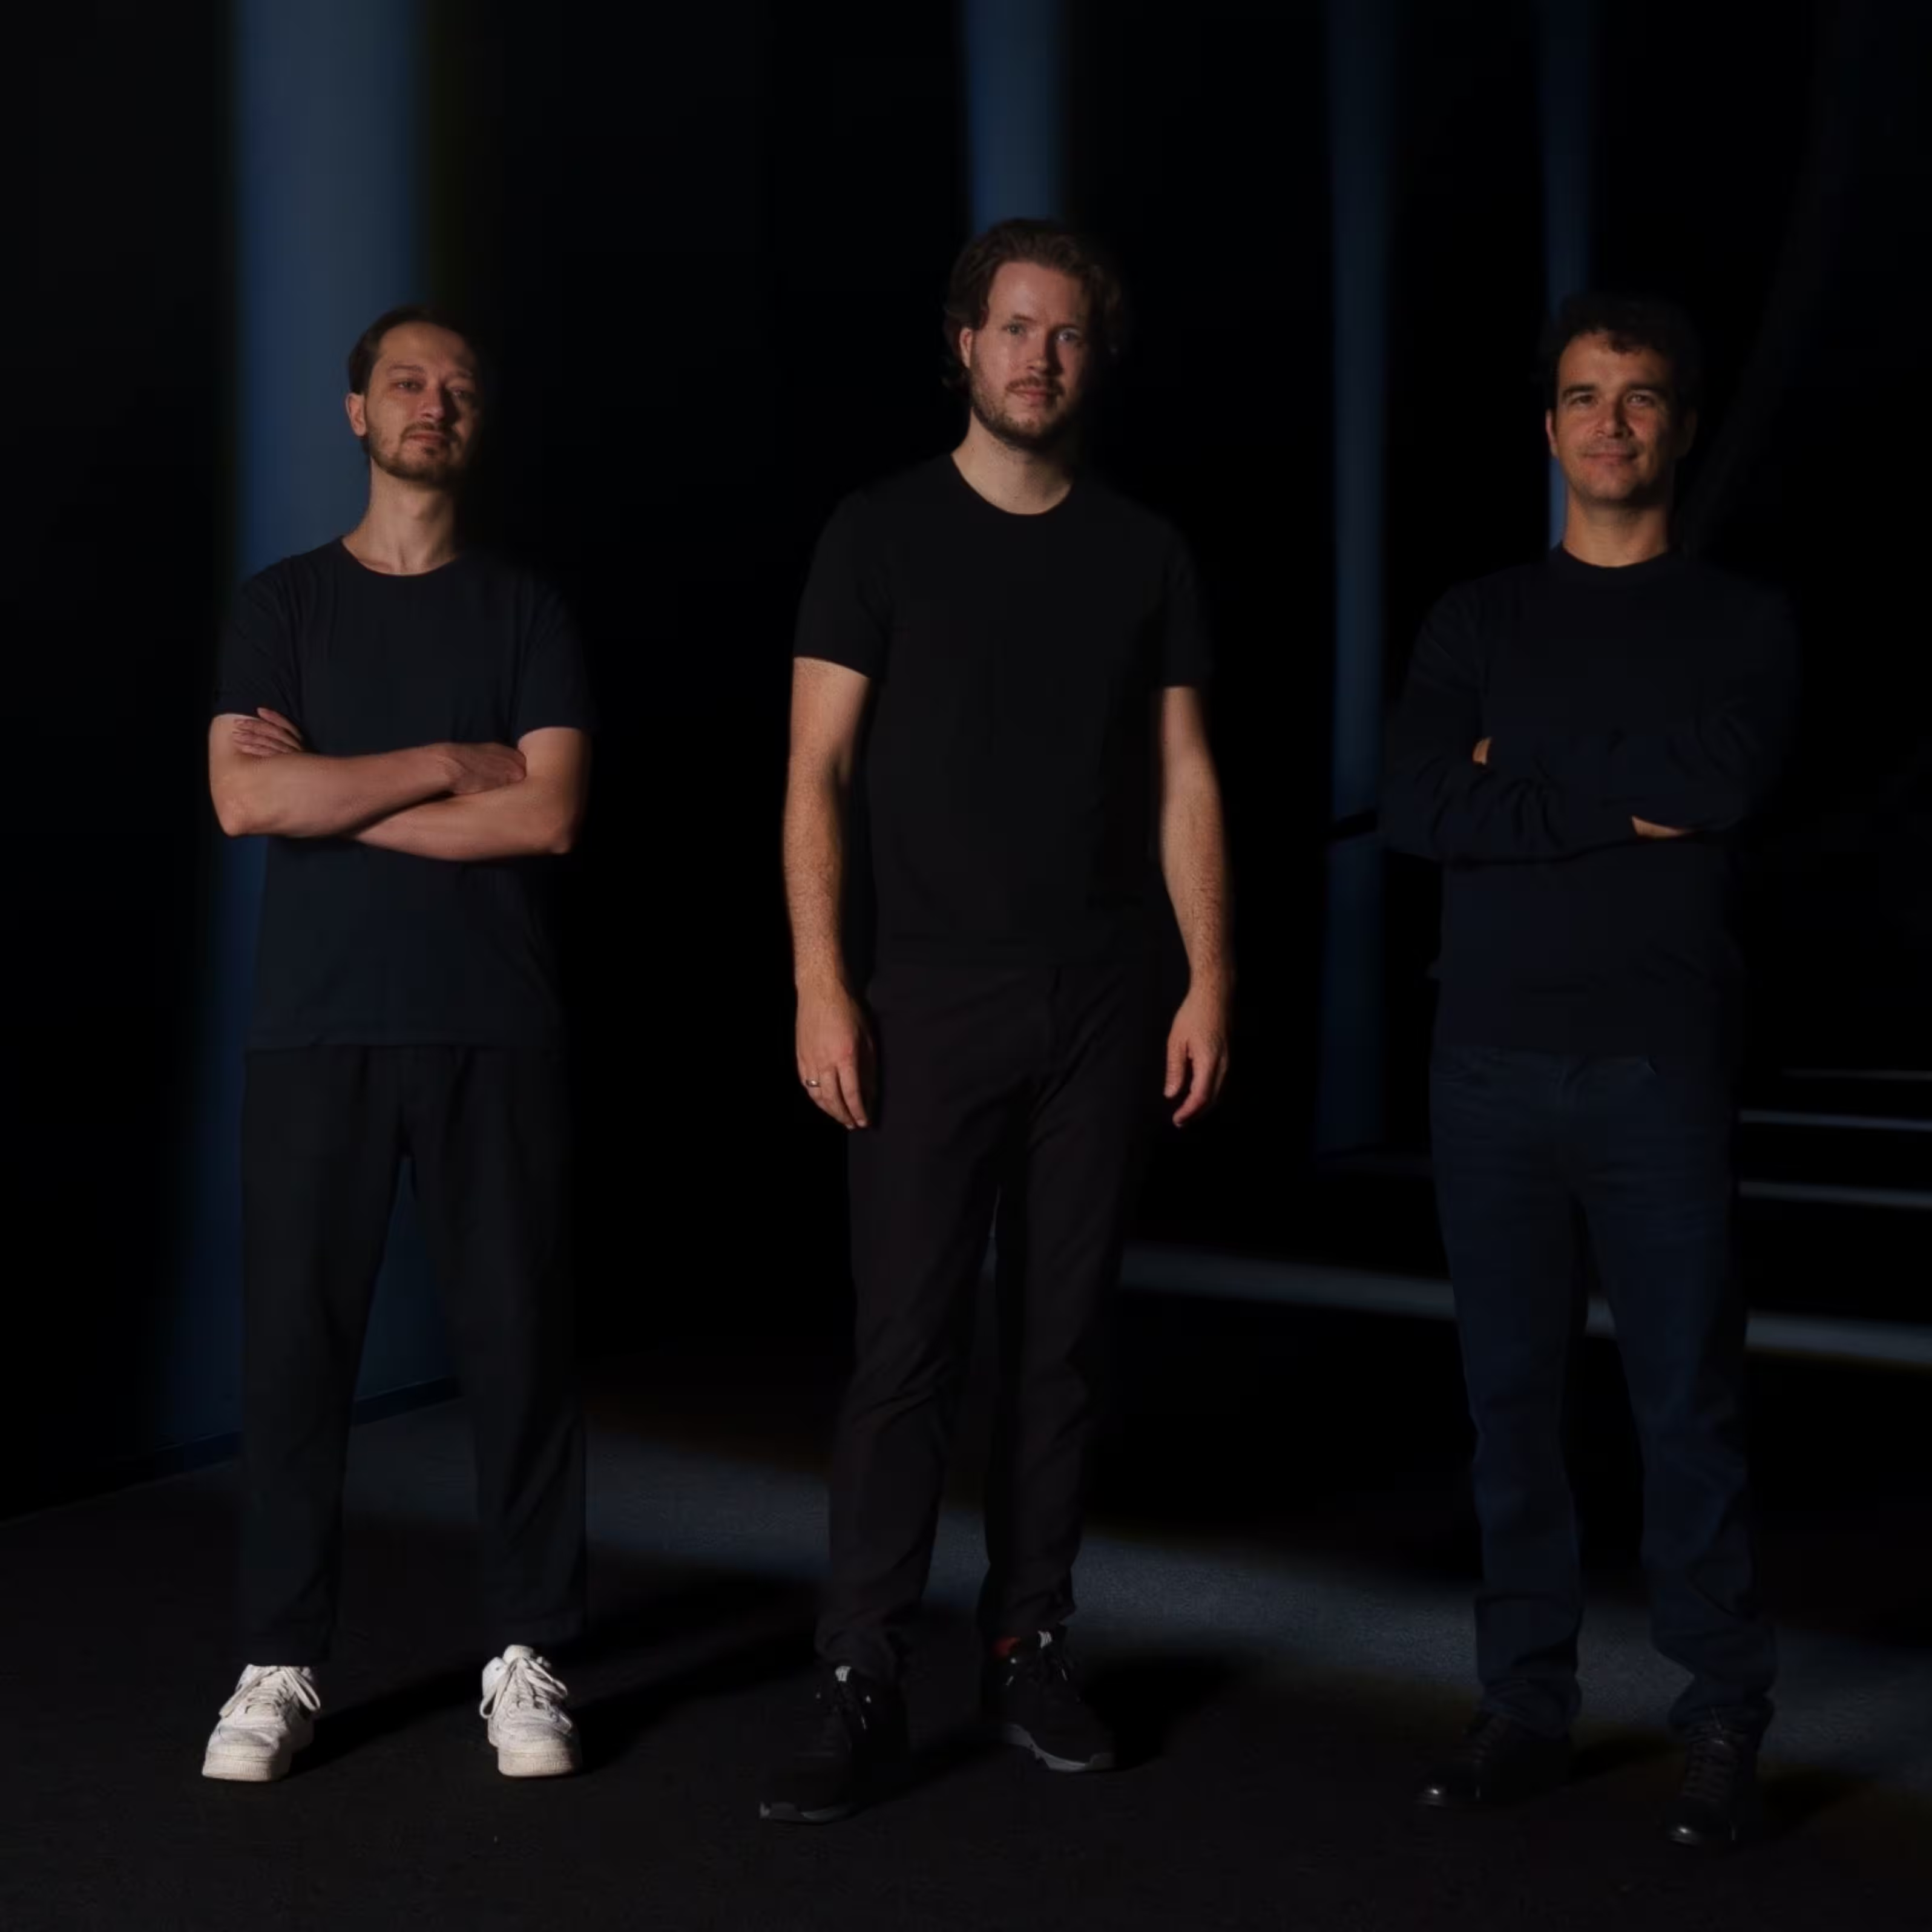
Hadrian founders Rogier Fischer, Olivier Beg and Maurice Clin

What we are building

We build AI agents that hack the way Rogier and Olivier did, at a scale no human team can match. They map what a company exposes online and try to break in the way an attacker would, around the clock. 

‍

We’ve built a continuous learning platform, with each insight feeding back to improve future testing. The hacker perspective continues to drive our product vision and roadmap.

A team member of Hadrian working on cybersecurity on his computer

Since 2021

Pioneers in AI offensive security

2021

Founded in Amsterdam to put the automation attackers use on the defenders' side.
13

The age at which our founders met online, in 2009, and started hacking.

300+

Enterprises worldwide whose security teams use Hadrian.

24/7

AI agents testing your attack surface the way real attackers would, around the clock.

3×

Named a Leader by GigaOm, three years in a row.

2026

Representative Vendor in the Gartner® Market Guide for Adversarial Exposure Validation.

Leadership Team

Rogier Fischer

Rogier Fischer

Co-founder and Chief Executive Officer

Olivier Beg

Olivier Beg

Co-founder and Chief Hacking Officer

Maurice Clin

Maurice Clin

Co-founder and Chief Business Development Officer

Gil Fromovitch

Gil Fromovitch

Chief Revenue Officer

Prash Somaiya

Prash Somaiya

Chief Technology Officer

Peter Hix

Peter Hix

Chief Operating Officer

Matan Shavit

Matan Shavit

General Manager, North America

Delano Lobman

Delano Lobman

Head of People

Rutger van Waveren

Rutger van Waveren

Head of Product

Ayanda Chiwuta

Ayanda Chiwuta

Head of Marketing

Klaas Meinke

Klaas Meinke

Head of AI

Melvin Lammerts

Melvin Lammerts

Head of Hacking

Our investors

Find out why our team rates us 4.8/5 to work for

We strive to create a work environment where everyone feels supported to grow, connect and have impact. Our work is creative, collaborative, bold and above all fun.

Frequently Asked Questions

Learn how Hadrian helps security teams find, verify, and fix what attackers actually exploit.

What does Hadrian do?

Hadrian is an agentic AI offensive security platform that helps modern security teams prevent breaches by continuously assessing the external attack surface, validating real-world threats, and prioritizing exploitable exposures. Agentic AI powers 10x visibility into your critical risks, cuts through false positives, and provides step-by-step remediation guidance. Organizations reduce time to resolution by 80%, reclaim 10+ hours weekly, and act before attackers can. With Hadrian, you don’t just keep up, you leave your adversaries in the dust.

Who should use Hadrian?

Security Operations teams and CISOs of medium and large enterprises who struggle with asset inventory, alert validation, and threat prioritization in their work processes.

How does Hadrian differ from traditional vulnerability scanners?

Unlike traditional tools that run periodic scans and produce high volumes of false positives, Hadrian operates continuously and autonomously. It uses an event-based agentic AI to mimic human hacker behavior, validating risks to ensure they are actually exploitable. This reduces noise and allows teams to focus only on verified threats.

What value can Hadrian provide SOC teams?

Hadrian empowers Security Operations Center (SOC) teams by shifting from passive vulnerability scanning to active adversarial validation, a process that drastically reduces alert fatigue by filtering thousands of theoretical alerts down to confirmed, exploitable threats. By automating the manual investigation workflow through AI-driven validation and generating undeniable Proof of Concepts (PoC), the platform allows analysts to bypass tedious triage and focus immediately on verified risks. This real-time, event-driven capability integrates seamlessly with existing SIEM and SOAR ecosystems to streamline response times , while simultaneously enriching security posture with proactive threat intelligence—ensuring continuous, high-fidelity visibility across the entire attack surface.