SubWiz is a lightweight machine learning model trained on millions of subdomains. Give it known subdomains and it predicts likely additions based on the naming patterns it finds, helping uncover assets that aren't present in passive sources.
OpenHack is an open-source workflow for AI-powered white-box security review. It works with coding agents including Claude Code, Codex, and Cursor to systematically investigate source code for security vulnerabilities.
The Exposure Clock shows how many exposures have been disclosed since any point in time, how many may be remotely exploitable, and how many have been added to CISA's Known Exploited Vulnerabilities catalogue.
SanicDNS is an open-source DNS resolver built for high-volume reconnaissance. With the right infrastructure, it can resolve millions of domain names per second, making large-scale DNS enumeration and subdomain discovery considerably faster.
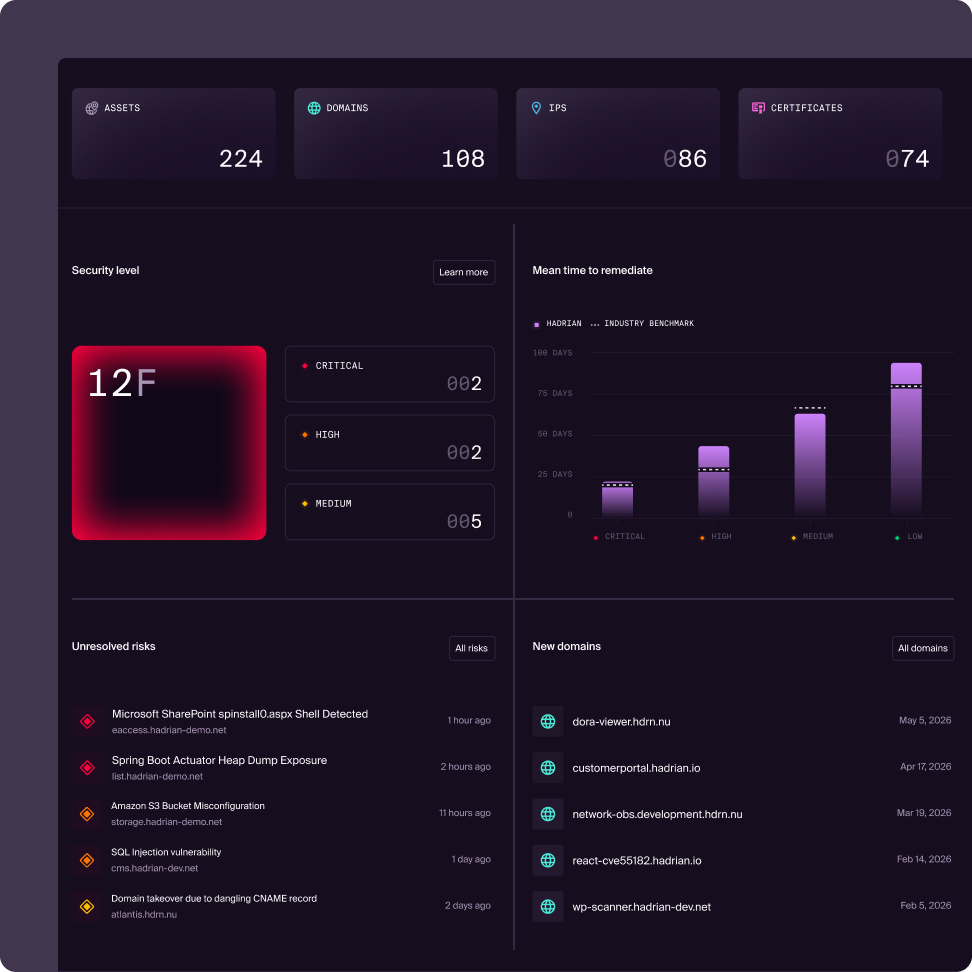
See Hadrian in action
Discover how Hadrian helps security teams find and validate vulnerabilities continuously and autonomously.