Agentic pentesting

Hundreds of hacker agents trained by elite ethical hackers to continuously discover, test, and validate your external exposures
Tried and trusted by:

McKesson logo
Siemens Energy logo
SHV Energy logo

No days off. No off days.

Traditional pentests take weeks to schedule and deliver a report that's outdated before it lands. Attackers now exploit new exposures within days of disclosure provides actionable insights, so a yearly test leaves the other 11 months unchecked. Hadrian delivers validated findings within hours of test initiation, at the same depth and quality every time. There's no dependency on which tester gets assigned, because no tester gets assigned.
Your schedule. Your scope.

Run a pentest after a release or ahead of an audit. You set the scope and change it when you need to, with no statement of work (SOW) to renegotiate and no procurement cycle to wait on. Because the cost allows for frequency, pentesting becomes something you run whenever the business needs it.

Hacker-trained. Battle-tested.

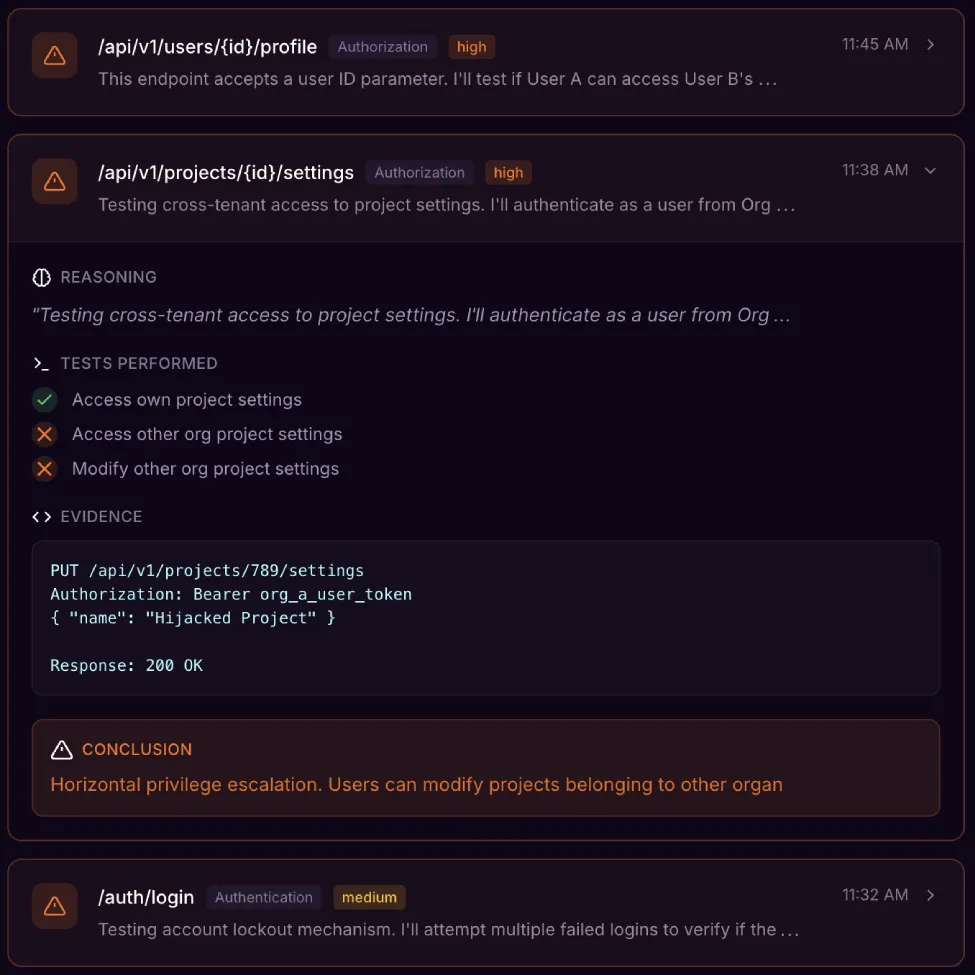
Hadrian's agentic AI is trained by elite offensive security practitioners. It learns your environment, maps your technology stack, and chains exposures together the way a skilled attacker would, building attack paths specific to your infrastructure. Every finding that reaches you comes with reproduction steps and execution evidence. Humans stay in the loop for scoping and run safety checks before higher-risk testing goes ahead.
See it in the product.

Click through a guided tour of the Hadrian platform: the same screens your team works in, with findings and the evidence behind them.

Trusted by companies globally

Trusted by SOC teams globally

All case studies
Damen Shipyards logo

Hadrian enables us to pinpoint the real security issues that we should be working on.

Hans Quivooij

CISO

London Business School logo

Event-driving testing saved time and energy with tests that leveraged insight

Danny Attias

LBS Chief Digital & Information Officer

SHV Energy logo

It's not often that you find a tool that homes in on the risks that truly matter

Mahdi Abdulrazak

Group Information Security & Risk Officer

Resources

Case Studies

How Budenheim strengthened continuous external security visibility

Case Studies

How Worldstream operationalized continuous exposure management across a critical infrastructure environment

Is Agentic Pentesting Right for You?

Guides

Is Agentic Pentesting Right for You?

Frequently Asked
Questions

Learn how Hadrian helps security teams find, verify, and fix what attackers actually exploit.

What does Hadrian do?

Hadrian is an agentic AI offensive security platform that continuously discovers your external attack surface and tests it for exploitable exposures. The platform deploys in minutes, operates autonomously, and delivers validated findings with reproduction steps and execution evidence. No agents to install, no infrastructure to manage.

What is agentic penetration testing?

Agentic penetration testing uses autonomous AI agents, trained by experienced offensive security practitioners, to find and exploit weaknesses across your external attack surface. Traditional pentesting relies on a single tester working a fixed scope over a few weeks. Agentic pentesting deploys hundreds of specialized agents that work in parallel, adapt their approach based on what they find, and concentrate depth where real exploitation paths exist.

How is this different from a traditional pentest?

Traditional pentests are point-in-time and scope-limited, and their quality varies with who gets assigned. They take weeks to schedule and deliver a report that's outdated before it lands. Hadrian runs on your schedule, covers your full external perimeter, and delivers validated findings in hours, with no procurement cycle or SOW. Results are consistent from one test to the next because they don't depend on an individual tester's skill or availability.

Does Hadrian replace manual penetration testers?

Hadrian handles the breadth and frequency that human testers can't sustain: continuous coverage across the full attack surface, on demand, with consistent quality. For specialized work such as red team exercises or deep application logic testing, human expertise still has a role. Many customers use Hadrian as their continuous baseline and bring in manual testers for targeted deep dives.

What does Hadrian test?

Hadrian tests your external attack surface, including domains, subdomains, web applications, APIs, cloud assets, login portals, and third-party and partner portals. Nova's agents also cover authenticated testing, authorization and insecure direct object reference (IDOR) testing, cross-tenant testing, business logic, and attack chains.

Is it safe to run against production?

You approve the scope before any test starts, and Hadrian's hackers run a safety check before higher-risk testing goes ahead.

Scalable solutions

Emerging threat response

Adversarial Exposure Validation

Continuous Attack Surface Management

Threat Exposure Management

Continuous pentesting

Automated red teaming

Cloud Exposure Visibility and Control

DNS Misconfigurations and Exposure

Acquisitions and subsidiaries

Leaked credentials and secrets

Remediation validation

Get a 15 minute demo

Experience Hadrian

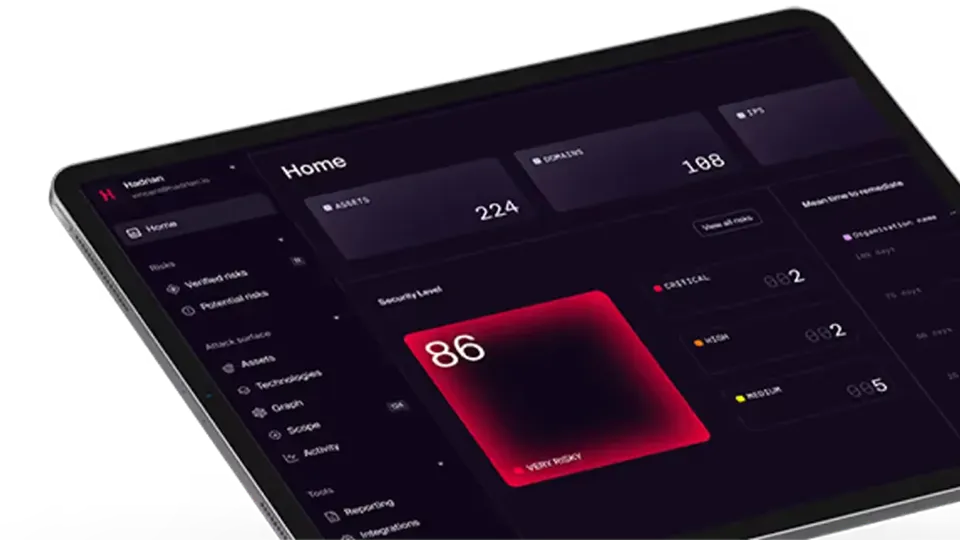
Hadrian’s end-to-end offensive security platform sets up in minutes, operates autonomously, and provides easy-to-action insights.
What you will learn

Monitor assets and config changes

Understand asset context

Identify risks, reduce false positives

Prioritize high-impact risks

Streamline remediation