Acquisitions and subsidiaries

Hadrian maps the external attack surface of every company in your group, including new acquisitions and legacy infrastructure, and starts testing it as soon as the deal closes.
Tried and trusted by:

McKesson logo
Siemens Energy logo
SHV Energy logo

Know what you're taking on

An acquisition brings domains, apps, and infrastructure that nobody on your team has tested. Hadrian maps the acquired company's external attack surface so exposures are known before its systems connect to yours.

Attribute every asset to the right company

In a large group, the hard part is knowing which domains belong to which company, and which don't belong to you at all. Hadrian attributes each asset to the right subsidiary or business unit, which cuts the clean-up work that comes from tools claiming assets you don't own.

Clean up legacy infrastructure

Mergers leave behind old MSP-managed servers and forgotten environments. Hadrian finds and tests them alongside the rest of your estate, giving you one view across the group while you consolidate.

See it in the product.

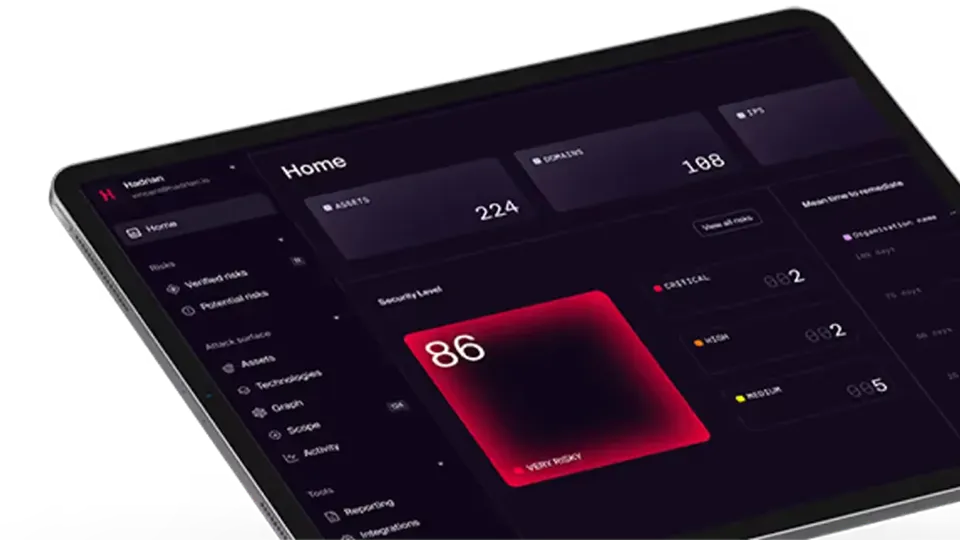
Click through a guided tour of the Hadrian platform: the same screens your team works in, with findings and the evidence behind them.

Trusted by companies globally

Trusted by SOC teams globally

All case studies
Damen Shipyards logo

Hadrian enables us to pinpoint the real security issues that we should be working on.

Hans Quivooij

CISO

London Business School logo

Event-driving testing saved time and energy with tests that leveraged insight

Danny Attias

LBS Chief Digital & Information Officer

SHV Energy logo

It's not often that you find a tool that homes in on the risks that truly matter

Mahdi Abdulrazak

Group Information Security & Risk Officer

Resources

Case Studies

How Budenheim strengthened continuous external security visibility

Case Studies

How Worldstream operationalized continuous exposure management across a critical infrastructure environment

Is Agentic Pentesting Right for You?

Guides

Is Agentic Pentesting Right for You?

Frequently Asked
Questions

Learn how Hadrian helps security teams find, verify, and fix what attackers actually exploit.

What does Hadrian do?

Hadrian is an agentic AI offensive security platform that continuously discovers your external attack surface and tests it for exploitable exposures. The platform deploys in minutes, operates autonomously, and delivers validated findings with reproduction steps and execution evidence. No agents to install, no infrastructure to manage.

Can Hadrian assess a company before the deal closes?

Hadrian can map a company's internet-facing assets using passive discovery. Active testing needs authorization from the asset owner, so it usually starts once the deal closes.
How does Hadrian tell which assets belong to which subsidiary?

Hadrian uses ownership signals from DNS, certificates, and registration records, and your team can confirm or correct attribution in the platform.

Can each subsidiary manage its own findings?

Yes. Role-based access lets each subsidiary or business unit see and act on its own assets, while the group security team keeps the full view.
Scalable solutions

Emerging threat response

Agentic pentesting

Adversarial Exposure Validation

Continuous Attack Surface Management

Threat Exposure Management

Continuous pentesting

Automated red teaming

Cloud Exposure Visibility and Control

DNS Misconfigurations and Exposure

Leaked credentials and secrets

Remediation validation

Get a 15 minute demo

Experience Hadrian

Hadrian’s end-to-end offensive security platform sets up in minutes, operates autonomously, and provides easy-to-action insights.

What you will learn

Monitor assets and config changes

Understand asset context

Identify risks, reduce false positives

Prioritize high-impact risks

Streamline remediation