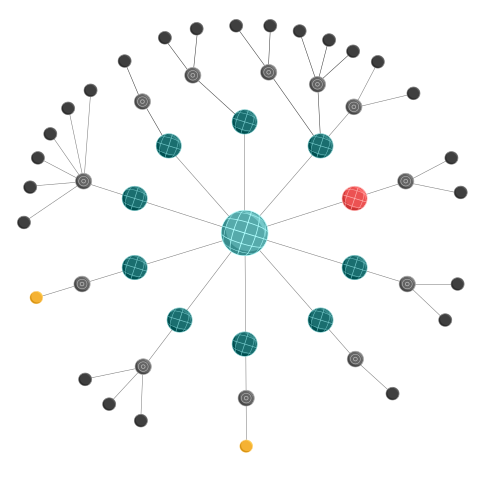
Atlas answers it, every day. It discovers every domain, DNS record, IP, certificate, cloud service and app you expose, then tests all of it the way an attacker would. You only hear about what is actually exploitable.
Trusted by companies globally



What do we actually have on the internet?
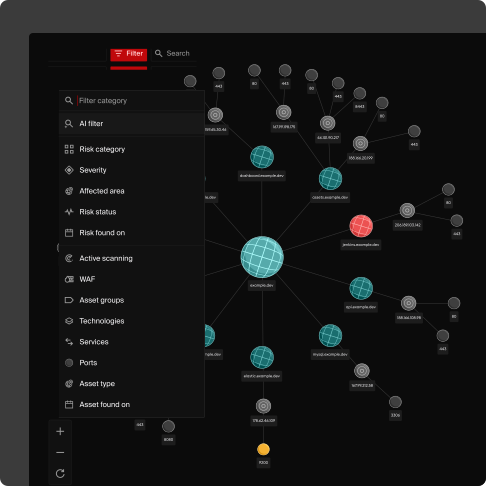
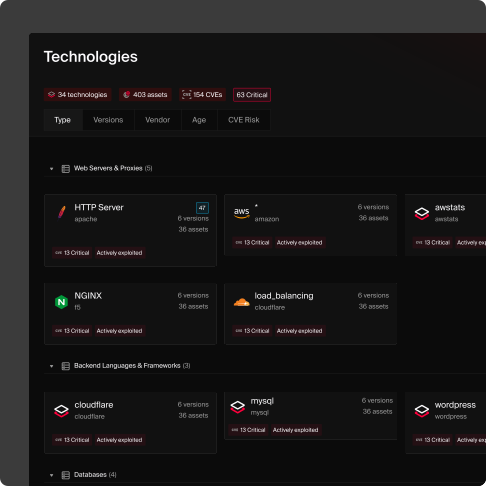
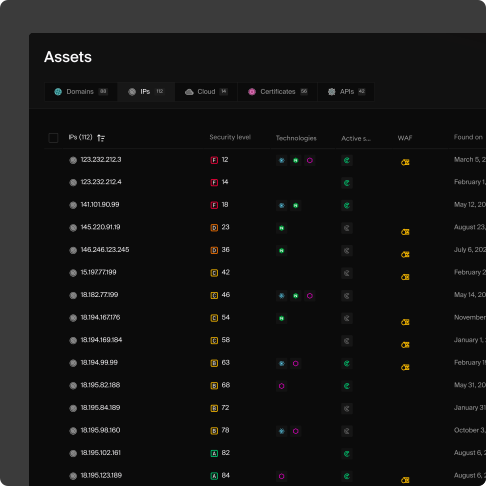
Atlas maps it. It starts with no scope and finds what belongs to you the way an attacker would, including the assets nobody remembers owning.
A CVE dropped this morning. Are we hit?
Atlas knows within hours. It matches the new CVE to the assets running the affected version, tests every one of them, and tells you which are really exposed.
Which of our alerts are real?
Only the ones Atlas can prove. Every potential exposure is validated before your team hears about it, so there is no triage queue full of maybes.


“It's not often that you find a tool that homes in on the risks that truly matter”
Mahdi Abdulrazak
Group Information Security & Risk Officer

“Event-driven testing saved time and energy with tests that leveraged insight”
Danny Attias
LBS Chief Digital & Information Officer
Hadrian Atlas | What it means for you | |
Looks at | Everything your company exposes on the internet | Domains, DNS, IPs, certificates, cloud services and apps, found from the outside |
Runs | Continuously | Passive discovery every hour, and new tests on every change |
Finds | Exploitable exposures | Chained and exploited the way a skilled attacker would, not pattern-matched |
When a CVE drops | Matched and tested within hours | You know which assets are affected while most teams are still reading the bulletin |
Validation | Every exposure, before you hear about it | No false positives, no wasted triage |
You get | A live inventory and a short list of verified risks | Prioritised by business context, not a generic severity score |
Proof looks like | Verified risks, with the evidence attached | Your team acts on facts, not maybes |
Deploys | From the cloud, in under 5 minutes | Nothing to install, nothing to maintain |
Priced on | Your total asset count | Add-ons for M&A assessment and infostealer leak detection |
What does Atlas do?
Atlas continuously maps your external attack surface and validates exposures. It discovers assets, technologies and service points, then uses agentic AI to confirm which exposures are actually exploitable.
How quickly does Atlas find new assets?
Passive scans run every hour. When a new asset or change is detected, event-driven testing kicks in automatically.
Do I get false positives?
No. Every exposure is independently validated before a notification is sent. Your team only acts on what is real and exploitable.
What are the available add-ons?
Atlas offers two add-ons at additional cost: mergers and acquisitions assessment and infostealers credential leak detection, which includes dark web scanning and credential leak monitoring.
How is Atlas priced?
Pricing is based on your total asset count. Reach out for a custom quote.
Who is Hadrian?
Hadrian is an offensive security platform used by security teams at 300+ enterprises worldwide. We were named a Representative Vendor in the 2026 Gartner Market Guide for Adversarial Exposure Validation and a Leader 3 years in a row by GigaOM.
See your attack surface the way an attacker does.
Book a demo and we’ll run Atlas against your own external attack surface.