Emerging threat response

Tens of thousands of CVEs are published every year, and the ones that matter are often exploited the day they go public. Atlas already knows what you run on the internet, adds new exploits within 24 hours and tests every asset they can reach, so you know if you're exposed before attackers find out.
Tried and trusted by:

McKesson logo
Siemens Energy logo
SHV Energy logo

Stop triaging CVEs that can't reach you

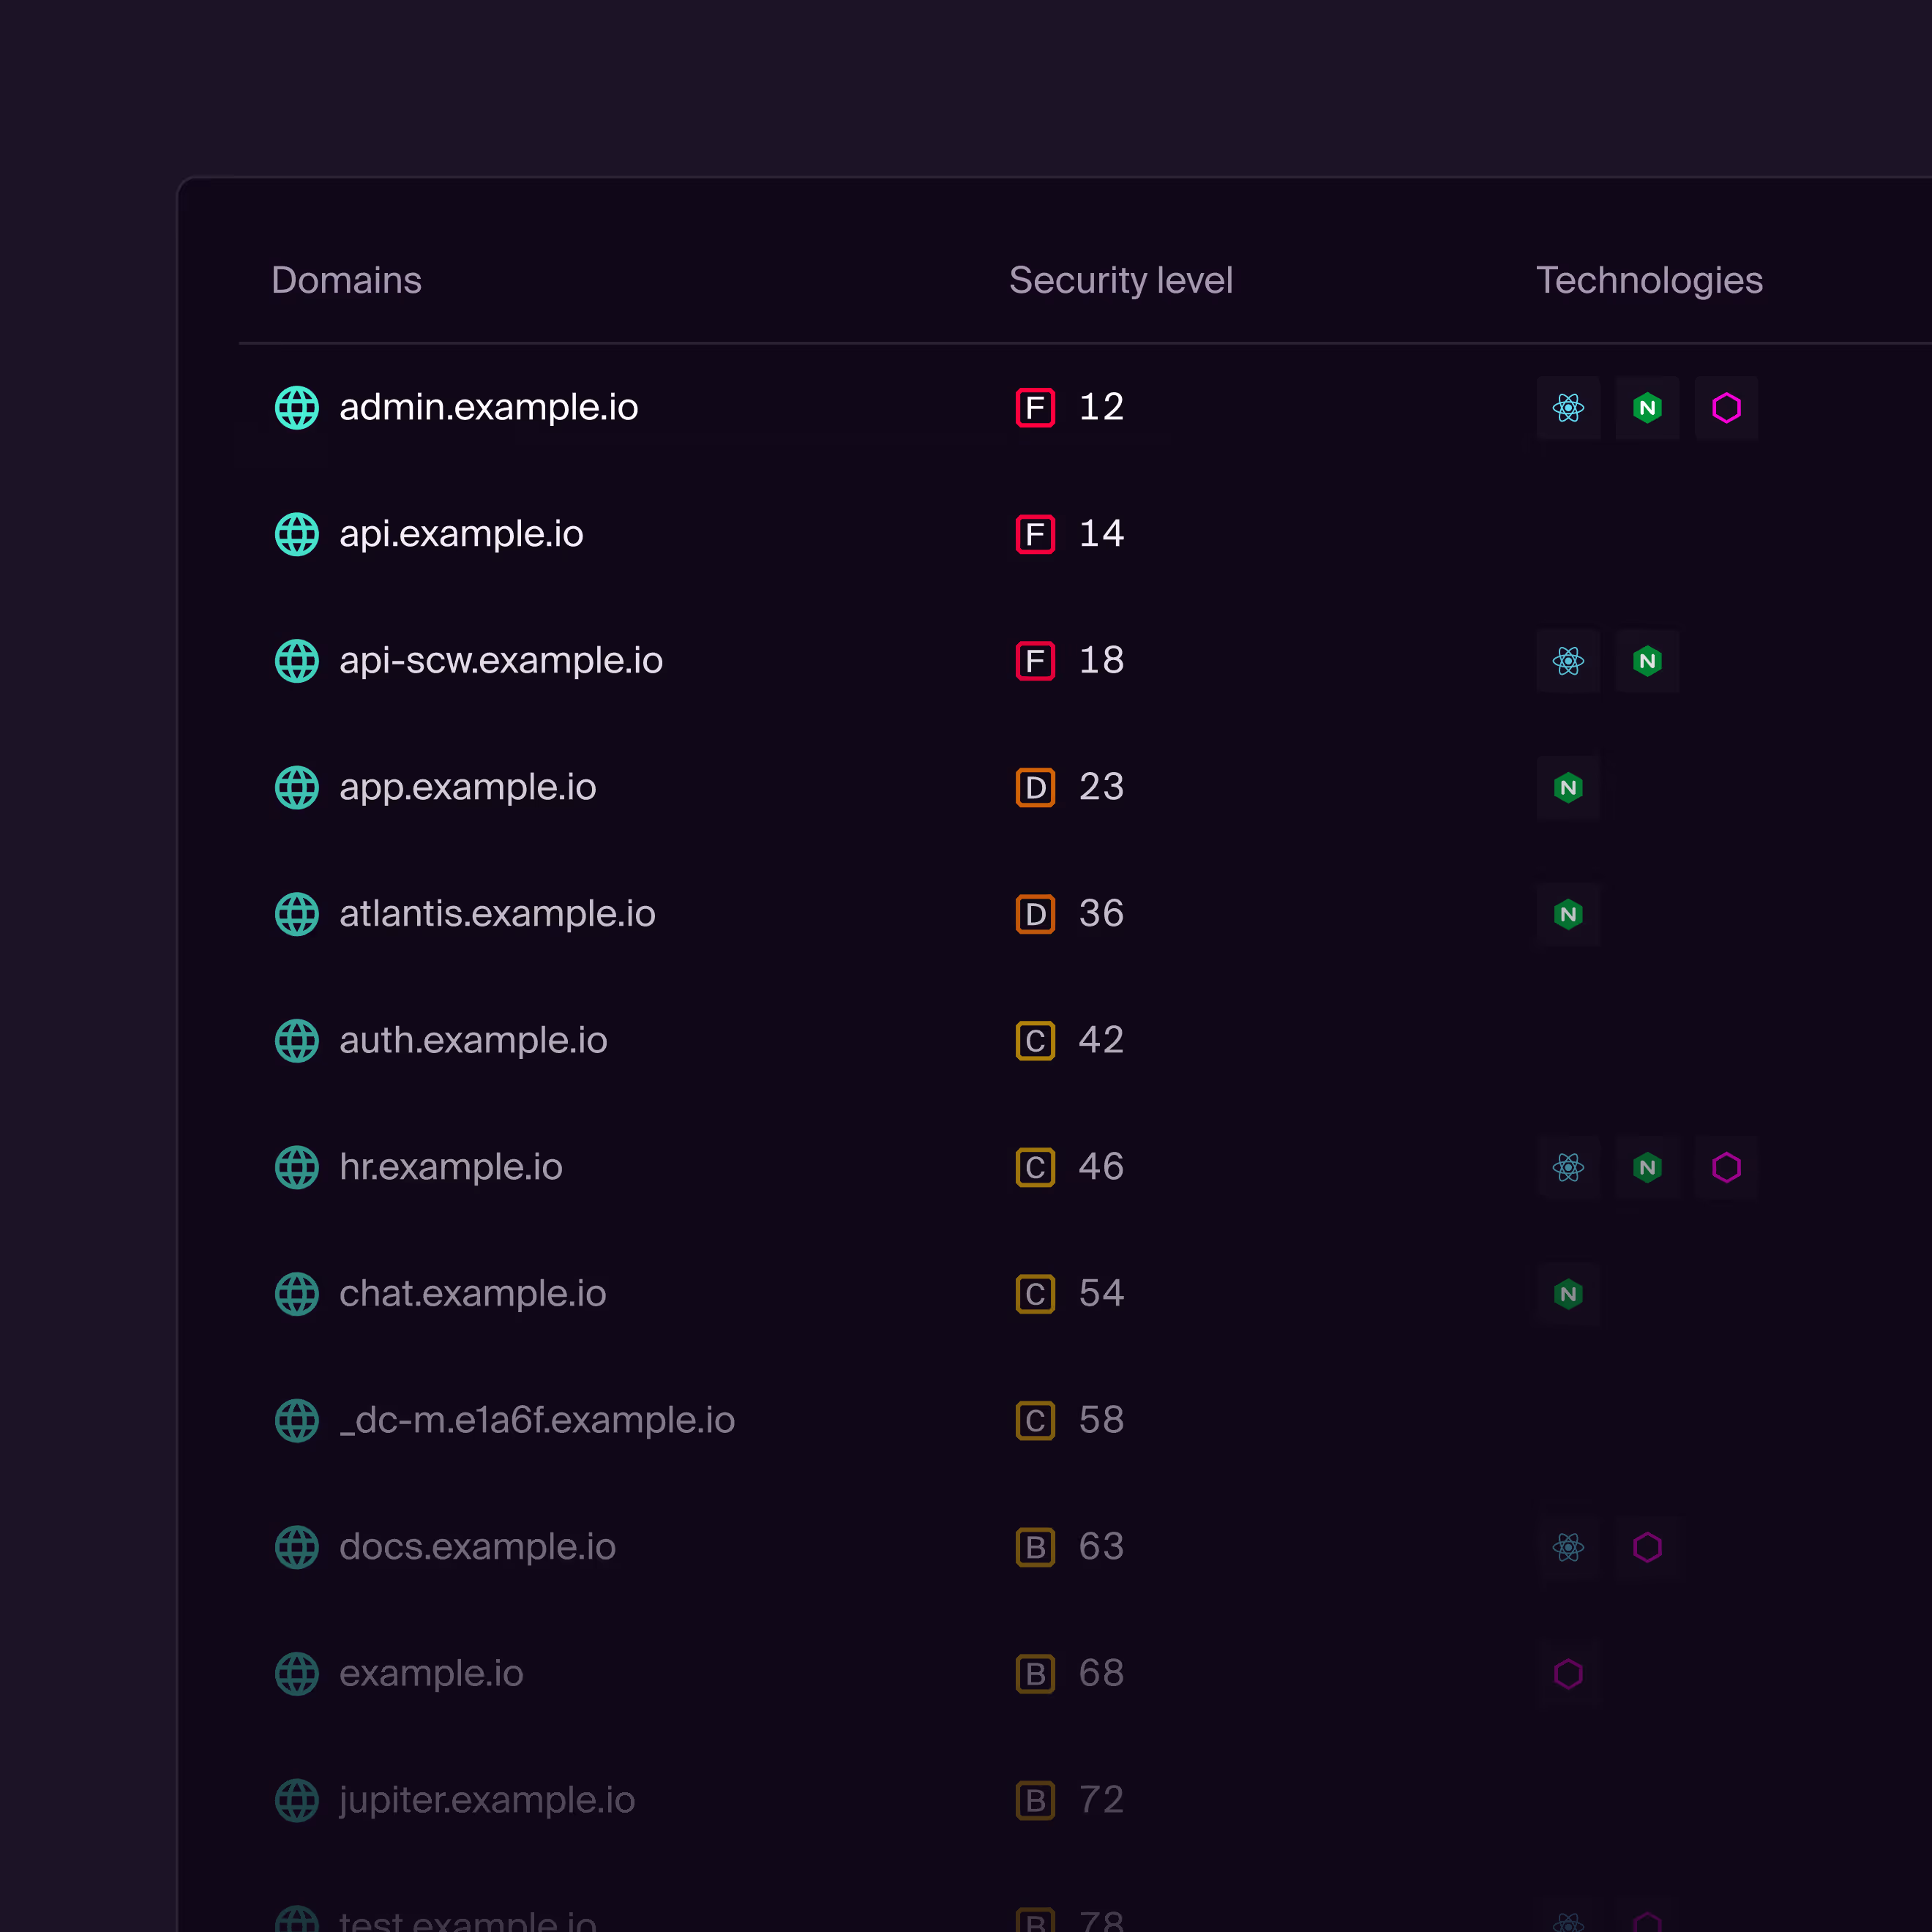
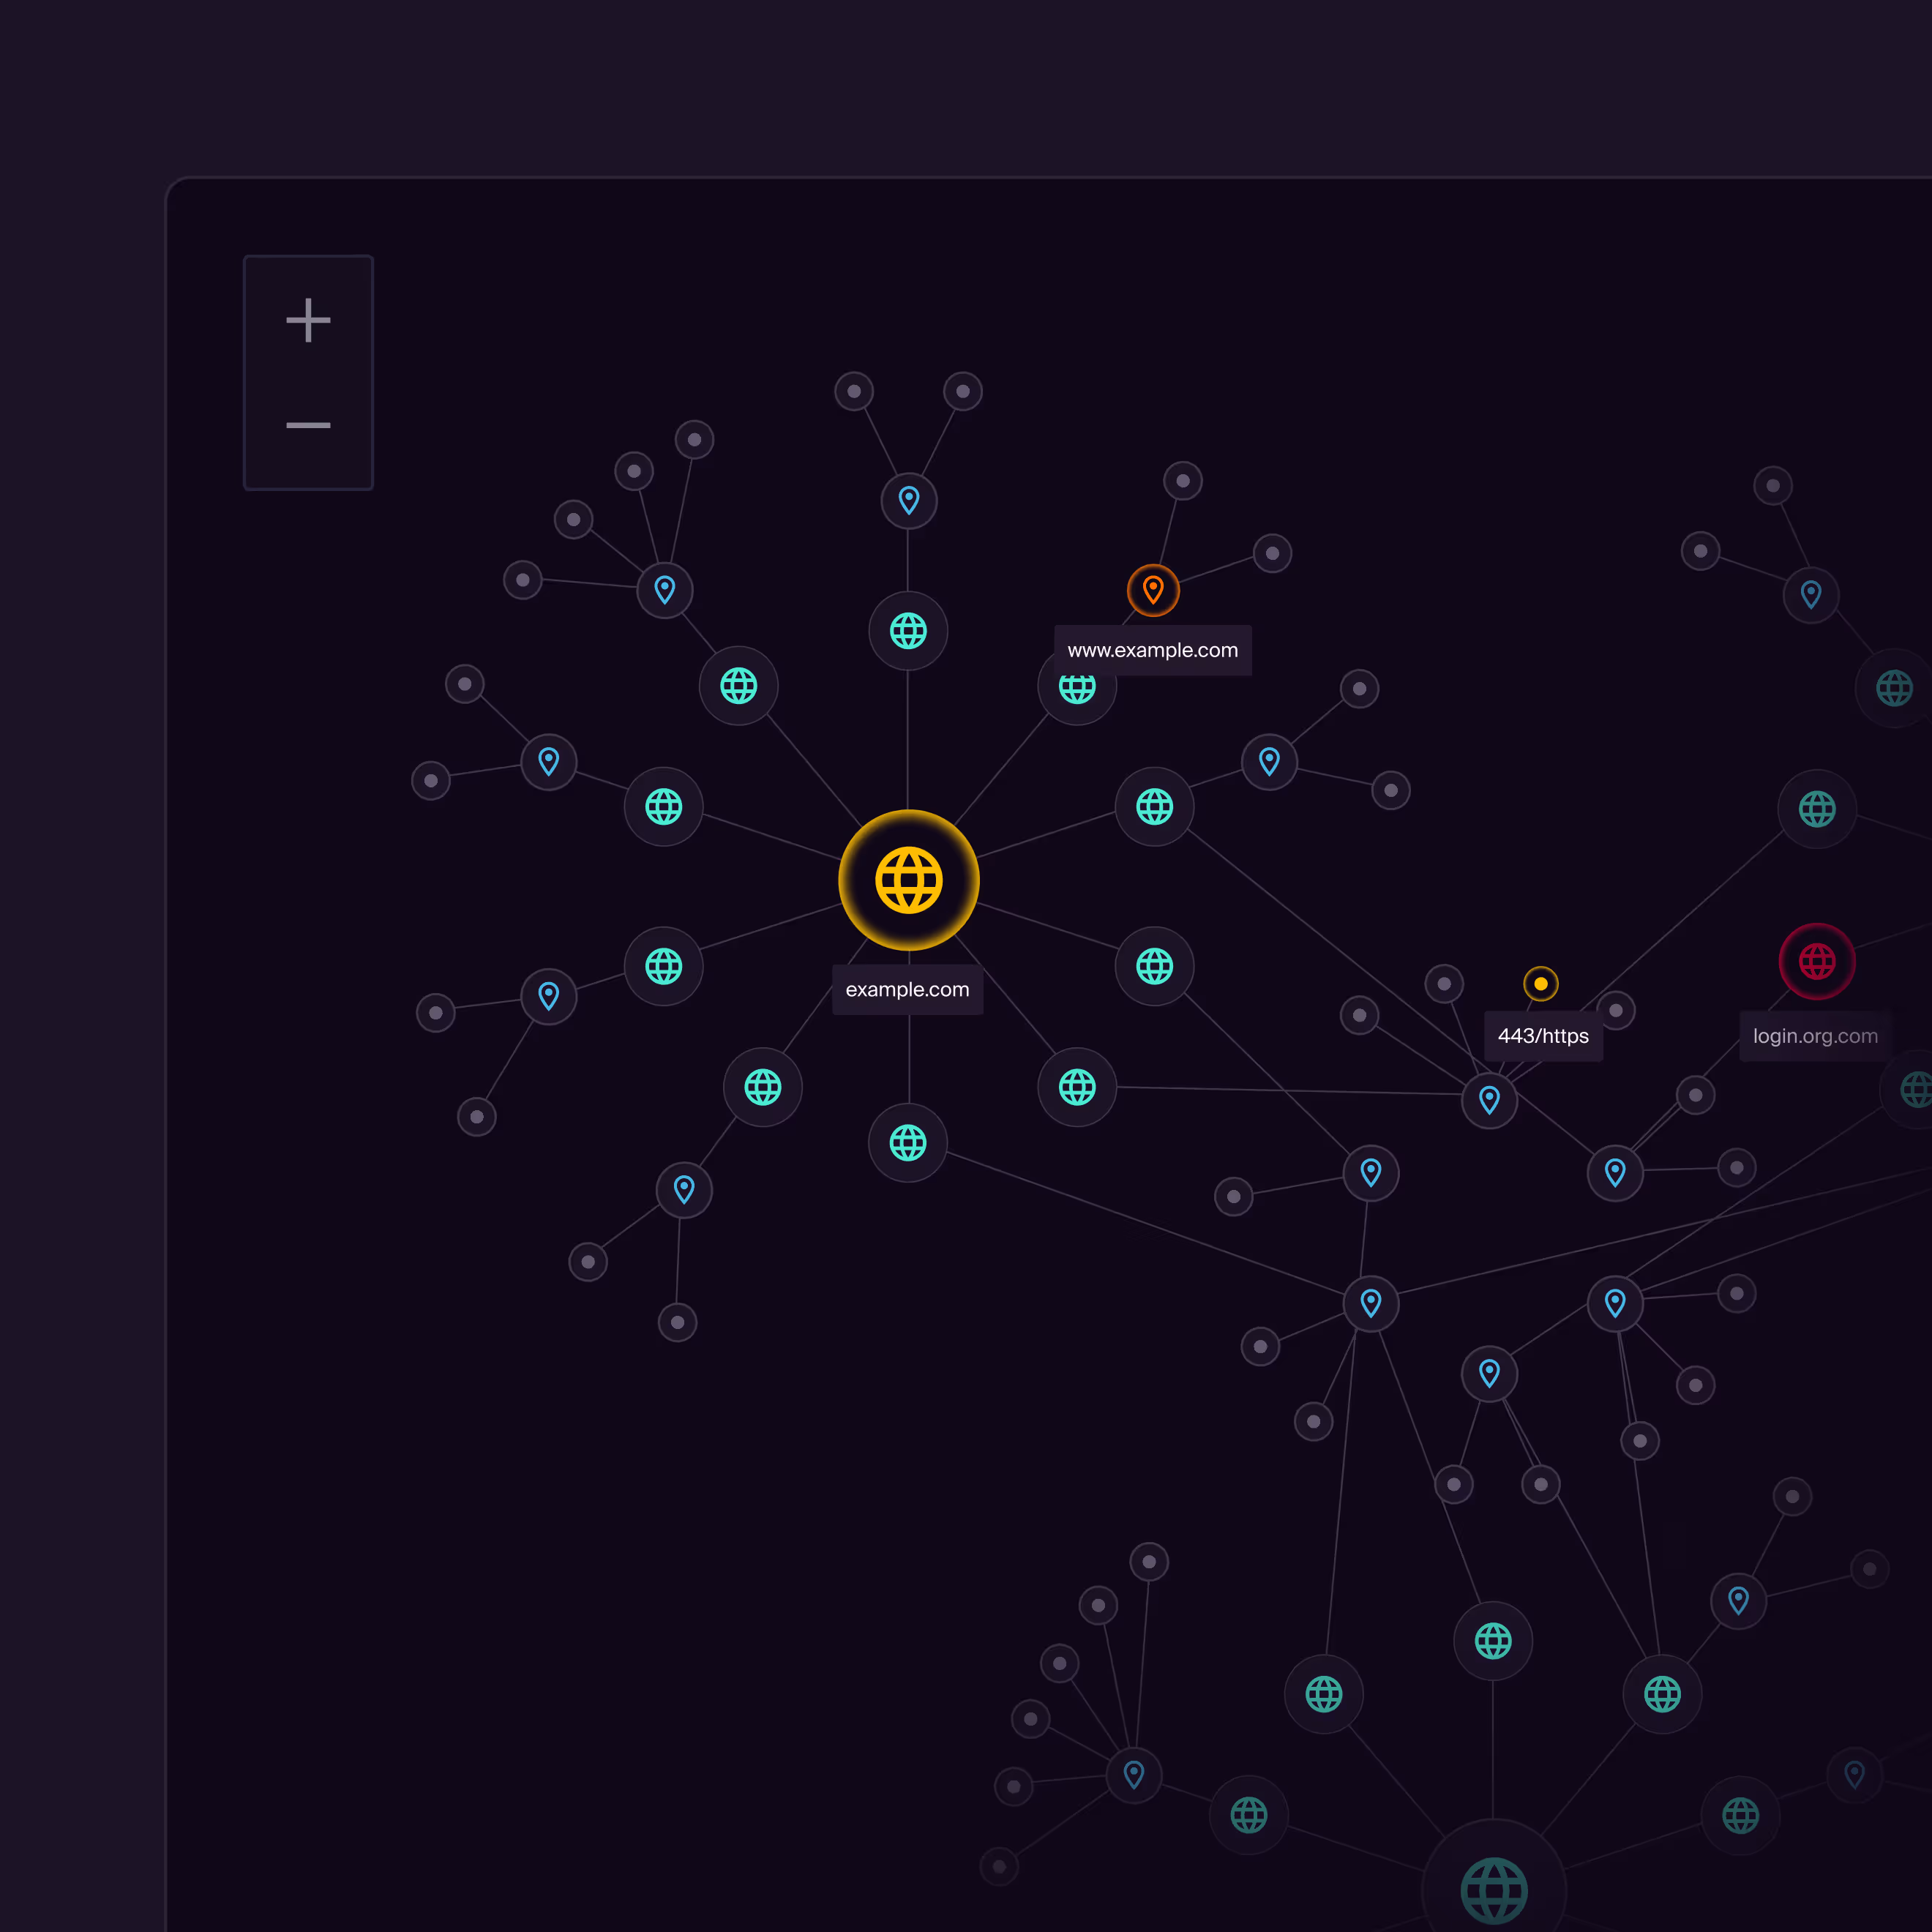
Zero Day Clock counted 30,000 new CVE records in the last quarter, against 11,000 in the same quarter a year earlier. No team can read every advisory, let alone patch against all of them. Atlas keeps a live inventory of your external assets and the software running on them, so each new disclosure is matched against what you actually expose, not a spreadsheet. Most CVEs drop out straight away. The few that touch your attack surface go to testing.

Test the day it drops, not at the next scan

In the first half of 2026, 137 vulnerabilities were already being exploited on the day they went public. A quarterly scan or a pentest booked weeks out can't keep up with that. When new exploits emerge, Hadrian's in-house ethical hackers add them to the platform within 24 hours, and Atlas's event-driven testing runs them against every matching asset straight away. There's no scan to schedule and no scope to agree.

Prioritise by proof, not by CVSS score

Severity scores help, but 60% of the vulnerabilities attacked within 90 days of disclosure were rated below critical, and honeypots still see daily attempts on flaws that are years old. Atlas exploits each match safely, the way an attacker would, and only alerts your team when the exposure is real, with the evidence attached. Older CVEs stay in the test set, so an asset that comes back online with a vulnerable version is caught too.

See it in the product.

Click through a guided tour of the Hadrian platform: the same screens your team works in, with findings and the evidence behind them.

Trusted by companies globally

Trusted by SOC teams globally

All case studies
Damen Shipyards logo

Hadrian enables us to pinpoint the real security issues that we should be working on.

Hans Quivooij

CISO

London Business School logo

Event-driving testing saved time and energy with tests that leveraged insight

Danny Attias

LBS Chief Digital & Information Officer

SHV Energy logo

It's not often that you find a tool that homes in on the risks that truly matter

Mahdi Abdulrazak

Group Information Security & Risk Officer

Resources

Case Studies

How Budenheim strengthened continuous external security visibility

Case Studies

How Worldstream operationalized continuous exposure management across a critical infrastructure environment

Is Agentic Pentesting Right for You?

Guides

Is Agentic Pentesting Right for You?

Frequently Asked
Questions

Learn how Hadrian helps security teams find, verify, and fix what attackers actually exploit.

How quickly does Atlas test for a newly disclosed vulnerability?

When new exploits emerge, Hadrian's in-house ethical hackers add them to the platform within 24 hours. Atlas then tests every asset running the affected technology straight away, without waiting for a scheduled scan.

Do we need to tell Atlas which assets run the affected software?

No. Atlas discovers your external assets continuously and identifies the technologies running on them, so it already knows where a new CVE could apply.

How is this different from a scanner's CVE feed?

A scanner matches version numbers against CVE lists and reports everything that might apply. Atlas attempts safe exploitation and only reports exposures it has validated, with evidence, so your team works from proof instead of possibilities.

How will we hear about a validated exposure?

Validated findings appear in the Hadrian platform with the evidence and remediation guidance, and can be sent to your ticketing, SIEM or messaging tools through our integrations.

Does Atlas still test for older vulnerabilities?

Yes. Attackers keep scanning for flaws that are years old, so Atlas does too. Older CVEs stay in the test set, and every change on your attack surface, such as a new host, port or software version, triggers new tests.

Scalable solutions

Agentic pentesting

Adversarial Exposure Validation

Continuous Attack Surface Management

Threat Exposure Management

Continuous pentesting

Automated red teaming

Cloud Exposure Visibility and Control

DNS Misconfigurations and Exposure

Acquisitions and subsidiaries

Leaked credentials and secrets

Remediation validation

Get a 15 minute demo

Experience Hadrian

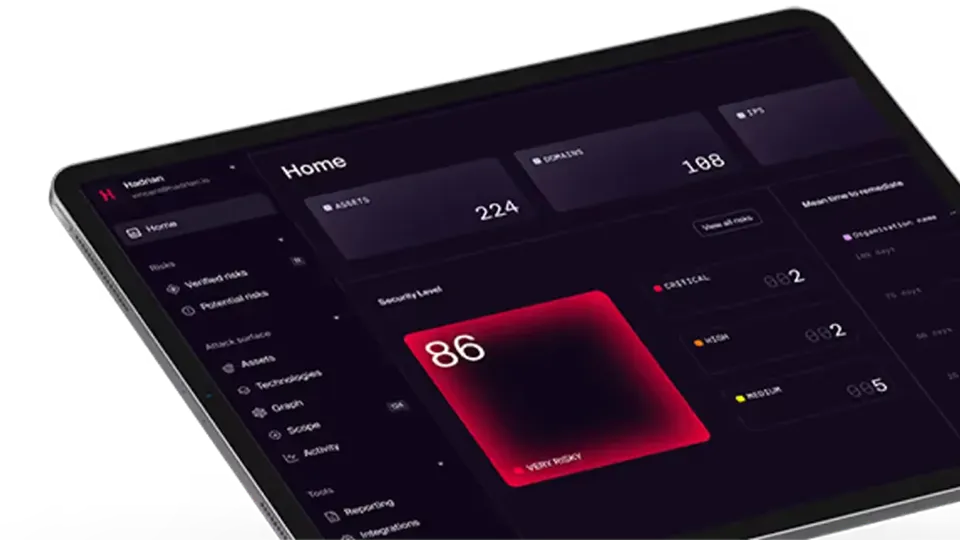
Hadrian’s end-to-end offensive security platform sets up in minutes, operates autonomously, and provides easy-to-action insights.
What you will learn

Monitor assets and config changes

Understand asset context

Identify risks, reduce false positives

Prioritize high-impact risks

Streamline remediation