Automated red teaming

A red team exercise shows how an attacker could get in during a few weeks of the year. Hadrian's hacker agents test your external attack surface continuously, chain what they find into attack paths, and report only the paths they can prove.
Tried and trusted by:

McKesson logo
Siemens Energy logo
SHV Energy logo

The attacker's view, every day

Attackers start from the outside, with no inventory and no scope. So does Hadrian. It discovers the domains, IPs, certificates, cloud services and apps tied to your organization, including the ones nobody remembers owning, and tests them whenever something changes. When Hadrian's ethical hackers add a new exploit, within 24 hours of it emerging, every affected asset is tested straight away.

Attack paths, not alert lists

A scanner reports issues one at a time. An attacker combines them. Hadrian's agents are trained by elite offensive security practitioners and chain exposures the way a skilled attacker would, building paths specific to your infrastructure. Only paths they can exploit reach your team, each with reproduction steps and execution evidence. From 1,000 assets scanned weekly, Hadrian pinpoints an average of 6 verified exploitable exposures.

Keep your red team on the hard problems

Hadrian doesn't replace a scoped red team exercise. Internal networks, social engineering and physical access stay with your human red team. Hadrian keeps your external attack surface under constant test between engagements, so your experts can spend their time where human judgment matters most. When one application needs deeper testing, Nova runs a full agentic pentest, from €1,250 per test.

See it in the product.

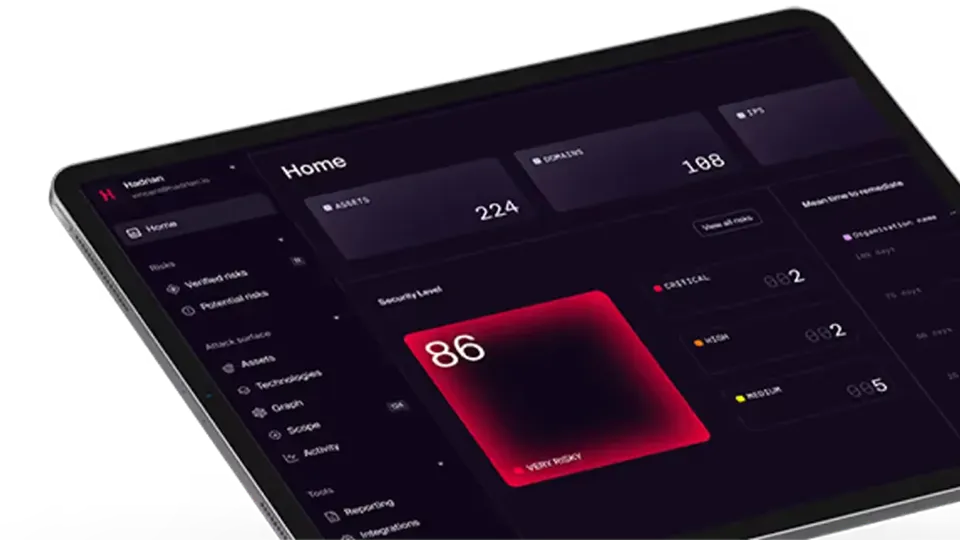
Click through a guided tour of the Hadrian platform: the same screens your team works in, with findings and the evidence behind them.

Trusted by companies globally

Trusted by SOC teams globally

All case studies
Damen Shipyards logo

Hadrian enables us to pinpoint the real security issues that we should be working on.

Hans Quivooij

CISO

London Business School logo

Event-driving testing saved time and energy with tests that leveraged insight

Danny Attias

LBS Chief Digital & Information Officer

SHV Energy logo

It's not often that you find a tool that homes in on the risks that truly matter

Mahdi Abdulrazak

Group Information Security & Risk Officer

Resources

Case Studies

How Budenheim strengthened continuous external security visibility

Case Studies

How Worldstream operationalized continuous exposure management across a critical infrastructure environment

Is Agentic Pentesting Right for You?

Guides

Is Agentic Pentesting Right for You?

Frequently Asked
Questions

Learn how Hadrian helps security teams find, verify, and fix what attackers actually exploit.

What does Hadrian do?

Hadrian is an agentic AI offensive security platform that continuously discovers your external attack surface and tests it for exploitable exposures. The platform deploys in minutes, operates autonomously, and delivers validated findings with reproduction steps and execution evidence. No agents to install, no infrastructure to manage.

Does automated red teaming replace our red team exercises?

No. Hadrian focuses on your external, internet-facing attack surface. Exercises that cover internal networks, social engineering or physical access still need a human red team. Hadrian keeps testing the external perimeter between those exercises.

How does Hadrian chain findings into attack paths?

Hadrian's agents learn your environment, including the technologies you run and the services you expose, and use it to decide what to test next. They combine exposures the way an attacker would and only report a path once they have exploited it, with reproduction steps and evidence.

Is it safe to test production systems continuously?

Hadrian uses safe exploitation to confirm that an exposure is real. Humans stay in the loop for scoping and run safety checks before higher-risk testing goes ahead.

How often does Hadrian test our attack surface?

Continuously. Passive discovery runs every hour, and any change on your attack surface, such as a new host, port or software version, triggers new tests.

Scalable solutions

Emerging threat response

Agentic pentesting

Adversarial Exposure Validation

Continuous Attack Surface Management

Threat Exposure Management

Continuous pentesting

Cloud Exposure Visibility and Control

DNS Misconfigurations and Exposure

Acquisitions and subsidiaries

Leaked credentials and secrets

Remediation validation

Get a 15 minute demo

Experience Hadrian

Hadrian’s end-to-end offensive security platform sets up in minutes, operates autonomously, and provides easy-to-action insights.
What you will learn

Monitor assets and config changes

Understand asset context

Identify risks, reduce false positives

Prioritize high-impact risks

Streamline remediation