Remediation validation

A ticket marked done doesn't mean the exposure is gone. When your team ships a fix, Hadrian tests it again the way an attacker would and closes the risk only when it can no longer be exploited, with the evidence to show for it.
Tried and trusted by:

McKesson logo
Siemens Energy logo
SHV Energy logo

Every fix retested

A finding isn't closed when engineering ships a fix. It's closed when the issue has been tested again. When your team marks a risk as resolved in Hadrian, it goes back for validation and Hadrian retests it the way an attacker would. If the exposure can no longer be exploited, the risk is closed automatically. If it still can, the risk stays open, so nobody signs off on a fix that didn't hold.

Evidence for every ticket and audit

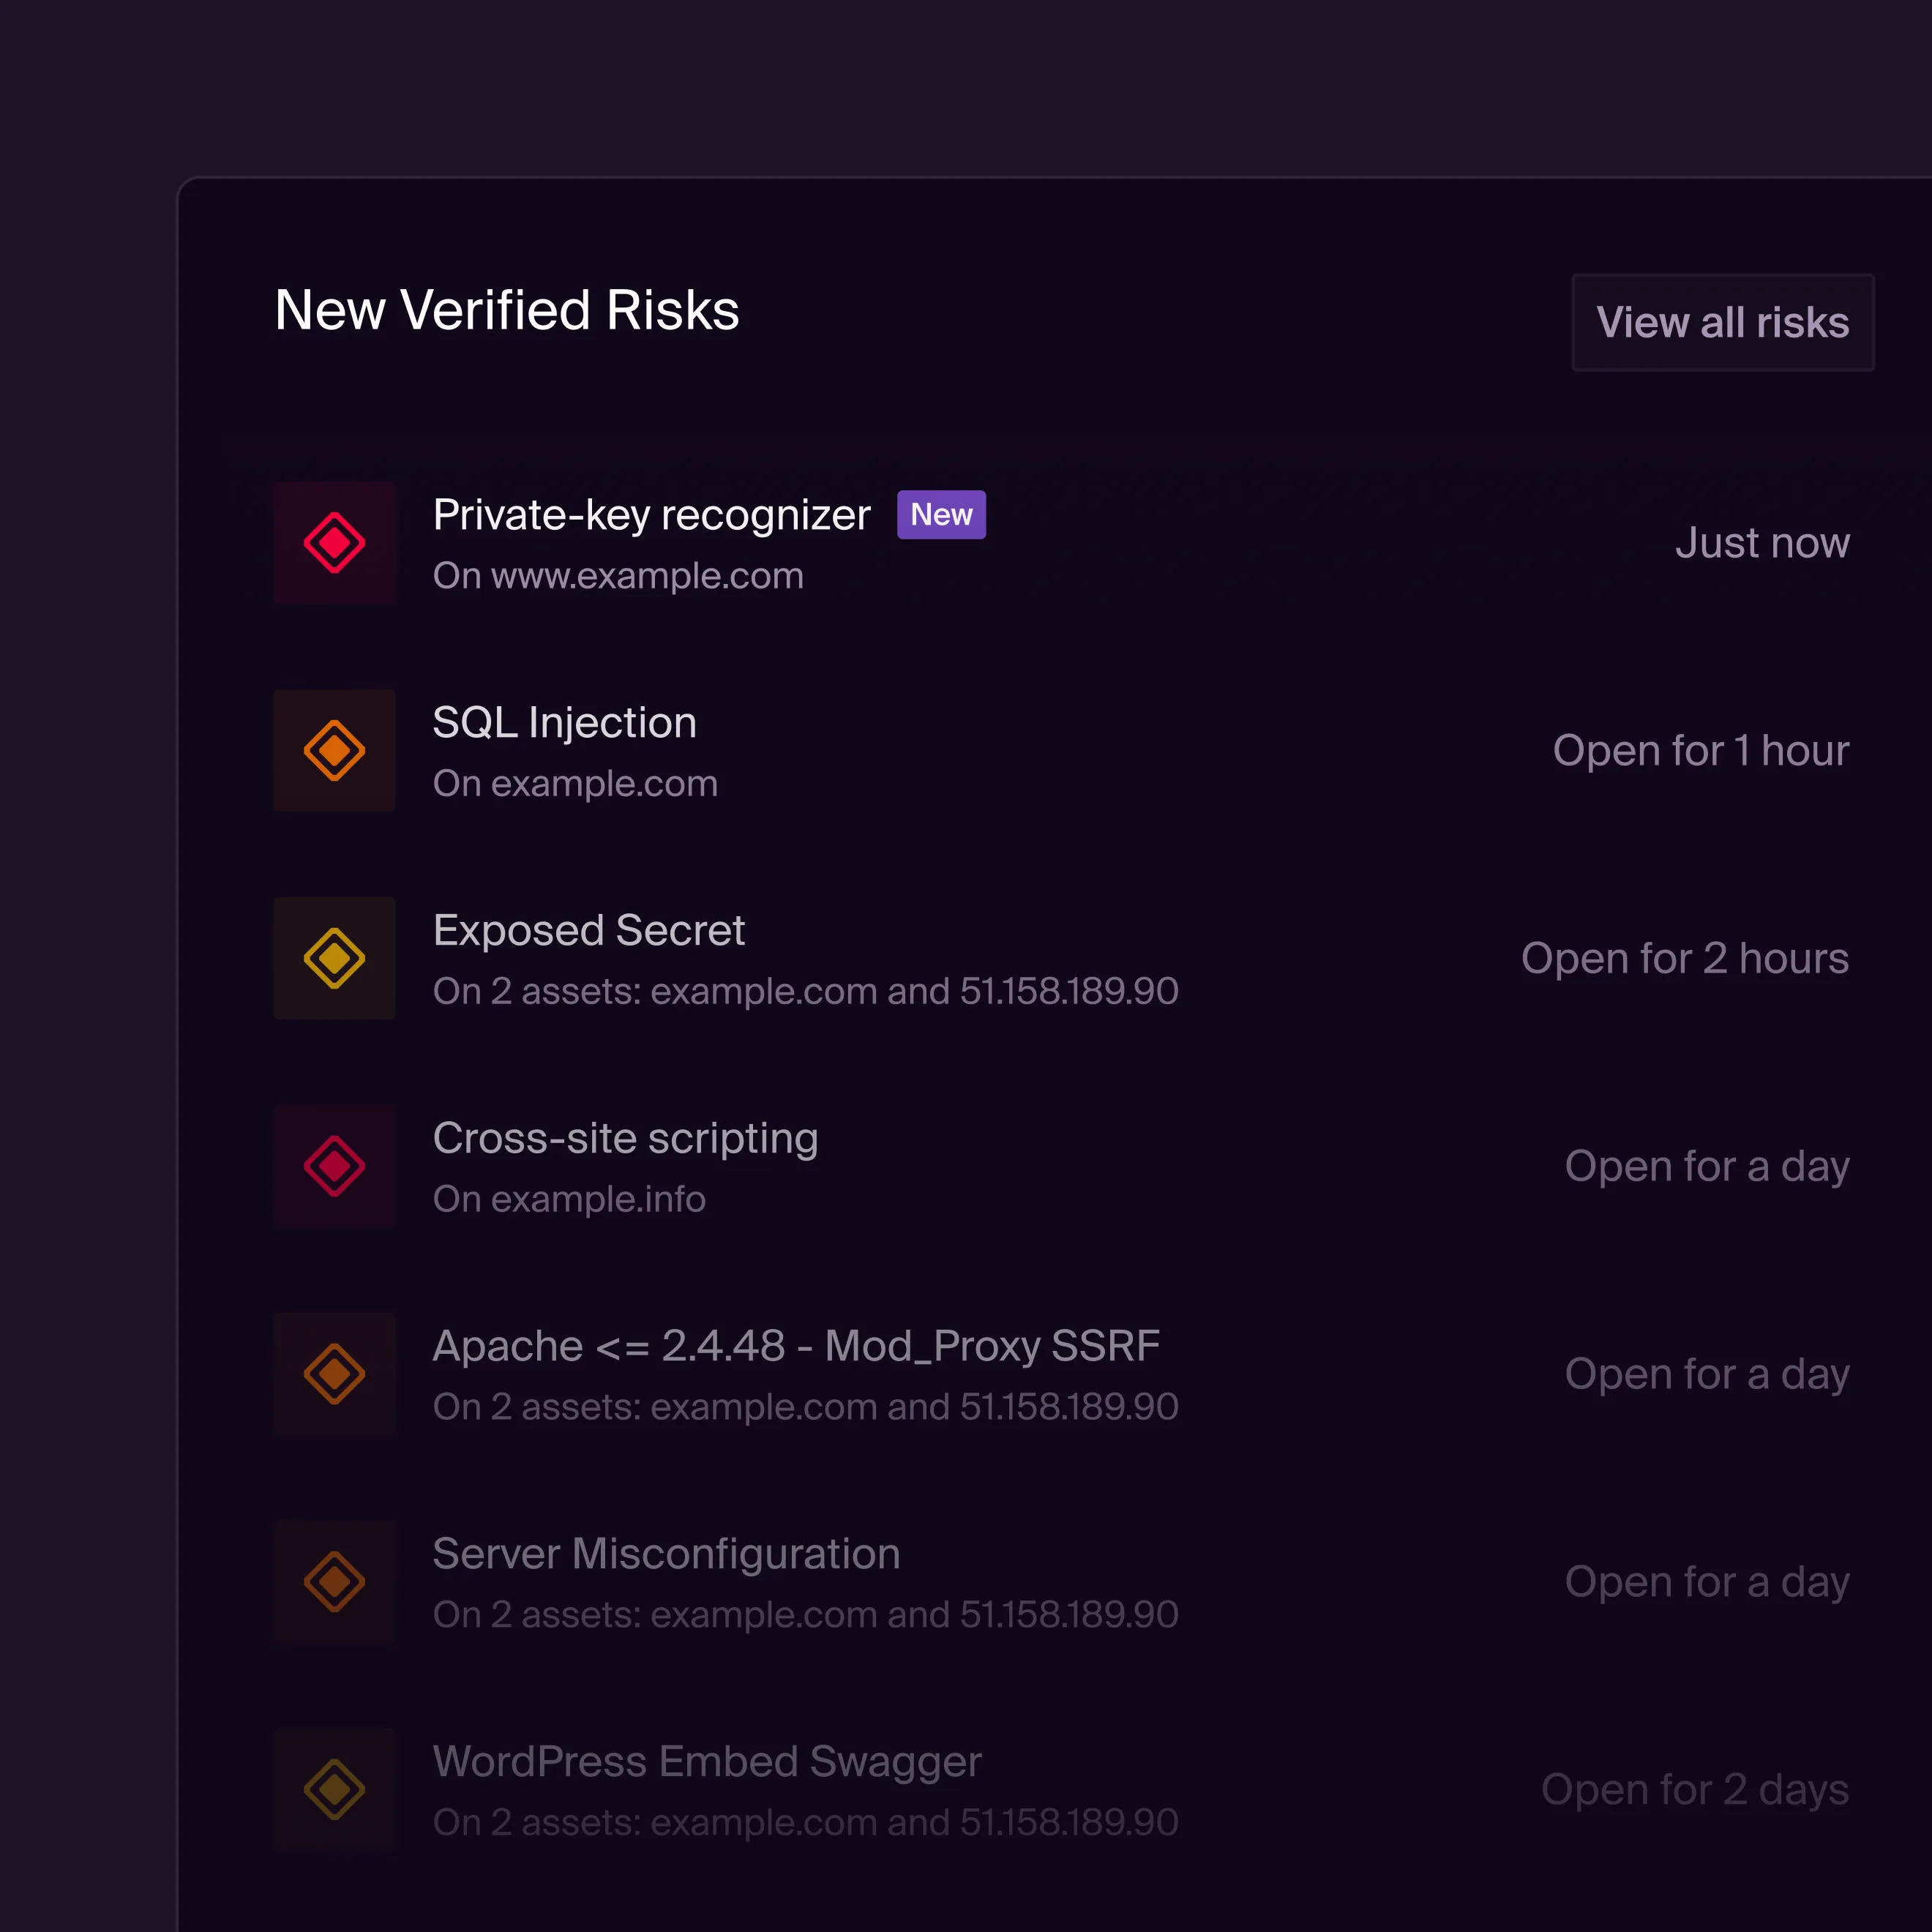
Every risk in Hadrian has its own page with severity, impact, a proof of concept and remediation steps, and it keeps its history from detection to closure. Findings go to the tools your teams already use, such as Jira, ServiceNow, Slack and Microsoft Teams, so engineers work from the proof. When an auditor or a third party needs to see it, share the risk securely or print it as a PDF.

Remediation SLAs you can prove

Only 33% of CTEM programs measure whether exploitable risk is actually reduced. Hadrian follows each risk from detection to validated closure, so mean time to remediate is measured on fixes that were proven, not on tickets that were closed. Reporting shows how your response times change over time, and the clear, reproduction-ready guidance helps teams cut mean time to remediate by up to 80%.

See it in the product.

Click through a guided tour of the Hadrian platform: the same screens your team works in, with findings and the evidence behind them.

Trusted by companies globally

Trusted by SOC teams globally

All case studies
Damen Shipyards logo

Hadrian enables us to pinpoint the real security issues that we should be working on.

Hans Quivooij

CISO

London Business School logo

Event-driving testing saved time and energy with tests that leveraged insight

Danny Attias

LBS Chief Digital & Information Officer

SHV Energy logo

It's not often that you find a tool that homes in on the risks that truly matter

Mahdi Abdulrazak

Group Information Security & Risk Officer

Resources

Case Studies

How Budenheim strengthened continuous external security visibility

Case Studies

How Worldstream operationalized continuous exposure management across a critical infrastructure environment

Is Agentic Pentesting Right for You?

Guides

Is Agentic Pentesting Right for You?

Frequently Asked
Questions

Learn how Hadrian helps security teams find, verify, and fix what attackers actually exploit.
What does Hadrian do?

Hadrian is an agentic AI offensive security platform that continuously discovers your external attack surface and tests it for exploitable exposures. The platform deploys in minutes, operates autonomously, and delivers validated findings with reproduction steps and execution evidence. No agents to install, no infrastructure to manage.

How does Hadrian confirm that a fix worked?

When your team marks a risk as resolved, Hadrian tests it again the way an attacker would. The risk is closed only when the exposure can no longer be exploited. If it still can, the risk stays open.

Do retests cost extra?

No. Retesting is built into the remediation workflow at no additional cost. Each Nova pentest includes unlimited retests within the first 12 months.

Which ticketing tools does Hadrian work with?

Hadrian integrates with ticketing and ITSM tools such as Jira, ServiceNow, Azure DevOps, Linear and GitHub, and with messaging tools such as Slack and Microsoft Teams. Other systems can connect through webhooks and the Hadrian API.

Can we use the results as audit evidence?

Yes. Each risk keeps its proof of concept, remediation steps and history, and you can share it securely or print it as a PDF. Nova pentests also include a compliance-ready report that maps results to frameworks such as SOC 2, ISO 27001 and NIS2.

Scalable solutions

Emerging threat response

Agentic pentesting

Adversarial Exposure Validation

Continuous Attack Surface Management

Threat Exposure Management

Continuous pentesting

Automated red teaming

Cloud Exposure Visibility and Control

DNS Misconfigurations and Exposure

Acquisitions and subsidiaries

Leaked credentials and secrets

Get a 15 minute demo

Experience Hadrian

Hadrian’s end-to-end offensive security platform sets up in minutes, operates autonomously, and provides easy-to-action insights.
What you will learn

Monitor assets and config changes

Understand asset context

Identify risks, reduce false positives

Prioritize high-impact risks

Streamline remediation